Beyond the Walls
As consumer products get smarter, how can manufacturers transfer security best practices from production environments into the devices in consumers’ hands?

Security measures are frequently addressed by manufacturers when designing and manufacturing increasingly intelligent products. Most of the efforts implemented are to protect the manufacturer’s network and production capabilities. But what happens beyond those secure walls? How does that effort continue even when a product leaves the protection of the factory?
Internet of Things
The Internet of Things movement has seen rapid acceleration and change as companies and individuals benefit from the many tasks these devices operate, the data they generate, and how they help facilitate connections between the users and their processes. This movement has seen steady growth with the adoption of smart home devices becoming more mainstream in people’s homes and an uptick in building management systems. A secondary reason for the spike in demand is improved efficiency, enhanced by the increased knowledge gained from the influx of data collected by these IoT sensors.
Enhanced data insights in production are a driving factor in the increased installation base, with around $100 billion in investments from the manufacturing sector alone. Estimates show that 127 new devices are connected to the internet every second, with an estimated $4–11 trillion in expected economic value. Current estimates also suggest that around 75 billion IoT devices will be installed by 2025, with 48 billion of those installed between 2020 and 2025 alone.
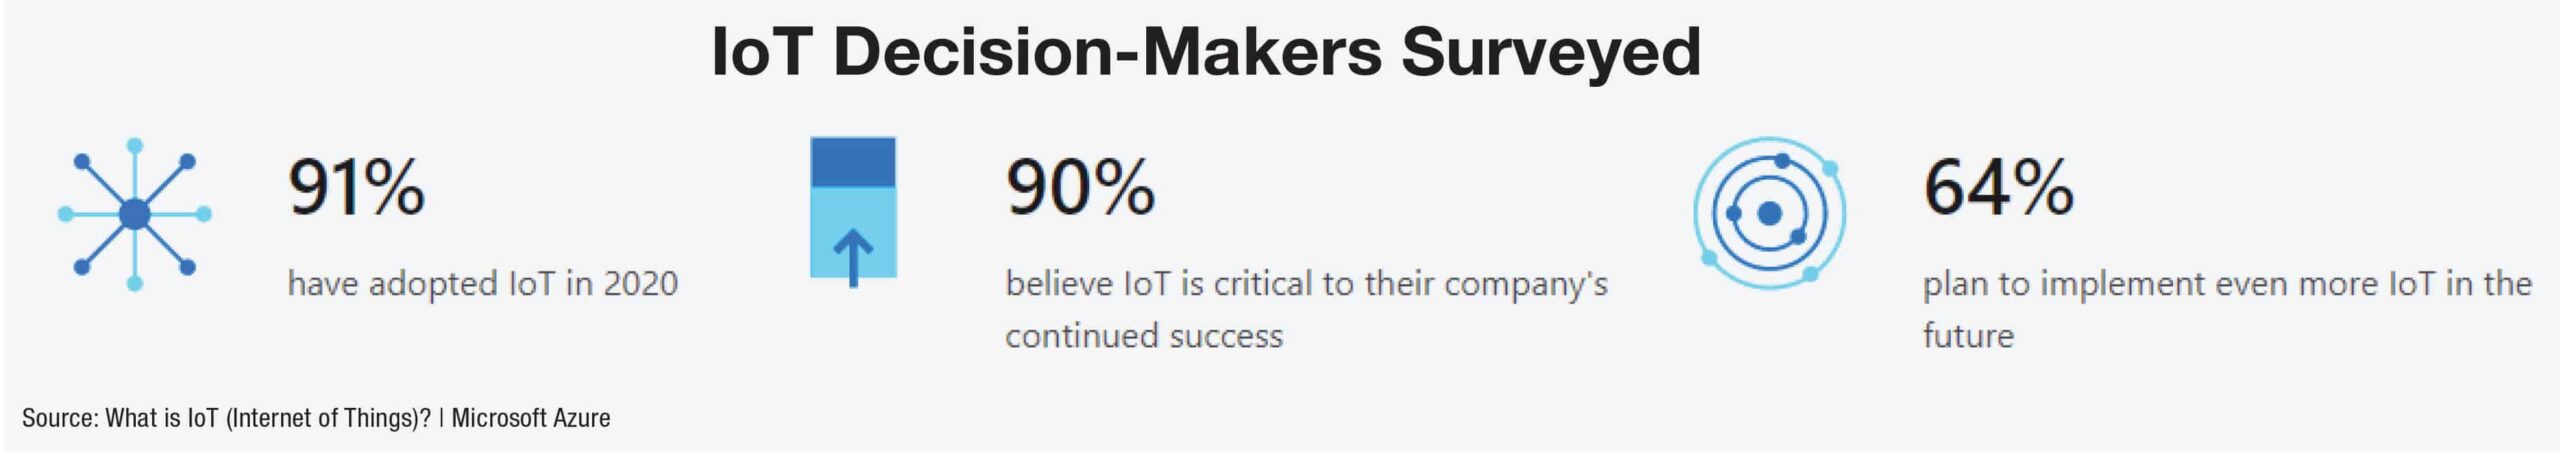
On the consumer side, simplifying daily chores and the promise of reducing costs via automation and data insights drive many home device purchases. From the enterprise perspective, real-time data has dramatically improved business efficiency leading to cost savings and increased profits. The return on the investment is relatively high compared to the current cost of most of these devices. While the benefits have proven worthy, the Internet of Things movement has left both producers and consumers more vulnerable and scrambling to offset these gains, searching for tools to improve insights into this newly connected part of the business.
The most crucial question is, what should manufacturers consider when creating secure IoT devices from the ground up? Not only do they want to focus on security during the design and creation, but on implementing security controls and ensuring those same controls ultimately carry over to the end user of the IoT devices. The focus on security for IoT devices usually is not a top priority for consumers who purchase these products, nor should it be. So, how can manufacturers now transfer their security best practices from their production environments into the devices they manufacture, and ultimately into their consumers’ hands?
Designing In Security
Great design starts with focusing on the product and how it will improve how we currently perform some tasks. Security needs to be part of the design process from the initial conversation of core software design into the actual product’s physical structure. The company’s security culture will dictate the whole process’s tone from start to finish, ensuring everyone understands the company’s mission around security will translate from the manufacturer to the end consumer. Manufacturers with a strong security culture will implement and address basic security controls early on. Elements such as passwords, encryption, two-factor authentication, biometrics, and zero trust frameworks provide an in depth defense strategy in the early stages. Each of these will allow the benefits to be carried over to the consumers’ hands to ensure that a product can support any strategy no matter what security approach is used in their own environment.
Software is a fundamental part of most IoT devices, and testing and securing the code is essential. Continuous improvements to the software allow for reductions in risk as the software is constantly changing and enhancing, increasing the difficulty of exploiting a vulnerability. Consumers can directly benefit from advances to the user interface (UI) and enhanced security developments from the updates provided. At this point, the data necessary for the product to function should be separated from usage information. The addition of encryption should also be a consideration so, in the unlikely event data is compromised, it poses another barrier to access. The main design goal should be that information cannot be traced back to the end user.
.